Operational fit
Security teams care about what happens after an alert. Who investigates it, who owns the next step and how it moves into the tools they already use?
Security buyers do not only want to see that you can find a problem. They need to understand how your product fits into their existing security stack, how much noise it creates, what data it touches and how their team gets from an alert to a real action.
A security purchase can involve analysts, security leaders, IT, developers, risk teams and procurement. Each group looks at the same product through a different lens.
Security teams care about what happens after an alert. Who investigates it, who owns the next step and how it moves into the tools they already use?
SIEM, EDR, IAM, ticketing, cloud platforms and developer tools are already in place. Integration depth matters more than a long logo slide.
Buyers want to know where the product runs, what permissions it needs, what data leaves their environment and where that data is stored.
A security leader needs to explain risk and progress to management, while analysts need enough detail to act on individual findings.
DemoRamp is a complete toolkit built around three areas with ongoing guidance and coaching for long-lasting, behavioral and organisational change.
Improve your teams communication, presentation and soft skills.
Build repeatable processes and clear rules around demos.
Practical, ready-to-use tools your team can apply in their very next demo.
Where cybersecurity demos usually go wrong. Here are the patterns that come up again and again.
Buyers see alerts, but not how their team investigates, prioritizes, assigns and resolves them.
Buyers want to know what happens with false positives, duplicate findings and hundreds of lower-priority alerts.
Agent, agentless, network access, cloud permissions and data collection can decide whether a project is possible at all.
Saying “we integrate with everything” without showing what data actually moves between the systems and whether the workflow works both ways.
A list of 10,000 findings is not useful if nobody knows which 20 to fix first.
Not every workflow deserves equal time. These are the things that matter most to Cybersecurity buyers.
Take one real security event from detection through investigation, prioritization, ownership and resolution.
Explain why one finding matters more than another and what evidence supports that decision.
Show permissions, data collection, hosting and the parts that stay inside the customer environment.
Create the ticket, enrich the alert or send the finding into the workflow the customer already uses.
Switch from analyst detail to management reporting and show how the same data supports both operational work and risk reporting.
Start wherever makes sense for your team’s maturity level. You don’t have to decide everything now. We can always expand later.
How good are our demos?
FreeLet’s start by reviewing a handful of your recorded demos, to see how you’re doing and where you need the most support.
See Demo ReviewHow can we see results from the very next demo?
Quick winQuick tips and better habits your team can use in the very next demo.
See Skills WorkshopHow do we make sure that everyone follows the same best practices?
RecommendedA full training and coaching program with guaranteed results, and your sales team involved.
See 90-Day AcceleratorAlso on its own: ENGAGED™ Demo WorkshopDemo Feedback ServiceOnline Demo CoursesCompare the options
Security people are paid to find gaps. They will challenge architecture, permissions, false positives, deployment and stack fit. If every technical question becomes a deep dive, the demo can turn into technical due diligence before the business risk is even clear.
“The demos that win are the ones that make the buyer’s real problem obvious first, and only then go deep into the detail.”Max LüpertzFounder, Presales Rockstars
Cheat sheets, checklists and guides to apply in your very next demo.
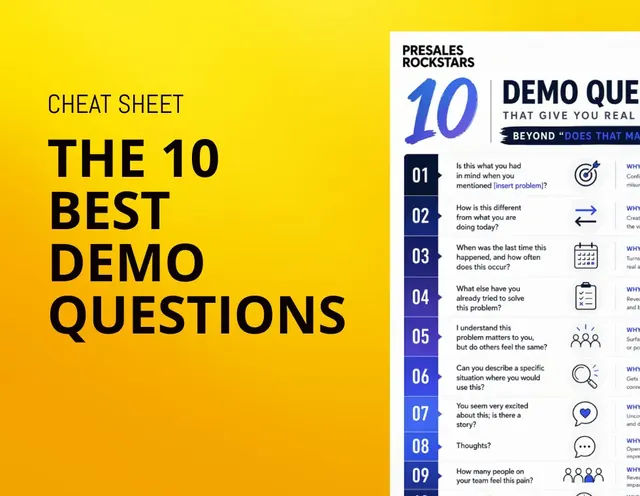 PDF · 1.3 MB
Meaningful and engaging demo questions beyond "Does that make sense?"
Download PDF · 1.2 MB
The most common objections and how to handle them
Download PDF · 246 KB
Detailed list of what questions (not) to ask during your demo
Download PDF · 1.7 MB
5 ready to implement steps that will improve your demo and demo process right away
Download PDF · 1.7 MB
How to build real trust with your clients by taking a genuine interest in their unknown challenges
Download PDF · 1.9 MB
Everything you need to know about MEDDPICC as a Solution Engineer
Download PDF · 126 KB
How to make sure that every demo request you and your team receives is properly qualified
Download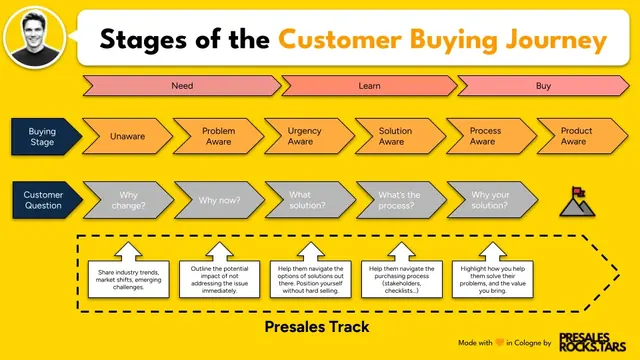 PNG · 102 KB
Understand your customers buying journey and what kind of input they need from you at every stage
Download PDF · 657 KB
How to better align internally on your demo objectives and narrative to make every demo count
Download PDF · 118 KB
Behaviours that make your customers trust you; or break it.
Download